Blog
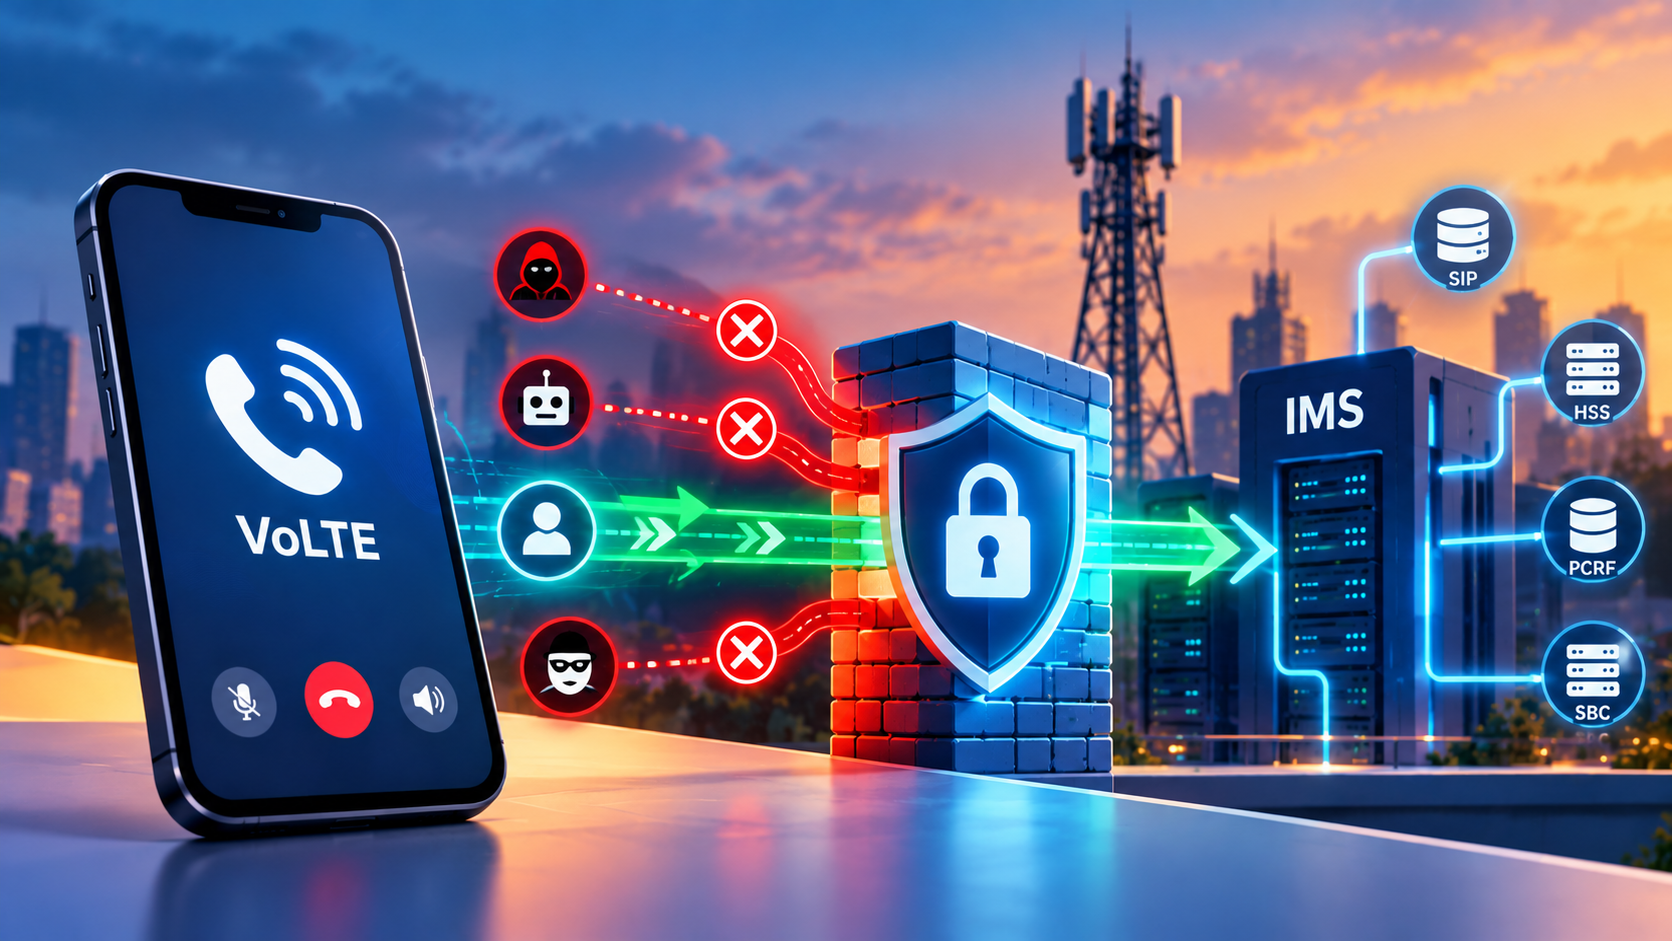
Voice over LTE (VoLTE) relies on the IP Multimedia Subsystem (IMS) and related network components to establish and manage voice sessions. These services exchange signaling and operational traffic across interfaces with different trust levels. If access rules are too broad or traffic is not filtered consistently, unauthorized IMS traffic may reach systems that should not accept it. VoLTE traffic filtering and access controls help operators limit unnecessary communication, protect service availability and reduce exposure to network misuse.
VoLTE traffic filtering is the process of allowing, restricting or inspecting network traffic according to defined security and service policies. It can include source and destination restrictions, port and protocol rules, signaling-aware validation, rate limits and monitoring for abnormal patterns. Filtering should reflect documented communication requirements rather than relying on broad assumptions that traffic from a familiar network is always trustworthy.
VoLTE network protection depends on clearly defined trust boundaries. IMS components may communicate with internal network elements, management systems, gateways and external partners. If any interface is exposed more broadly than required, it can increase the risk of unauthorized requests, misconfiguration or service disruption.
Start by documenting the IMS security architecture, including network elements, signaling paths, management interfaces, trusted peers and external connections. Record which systems need to communicate, the purpose of each flow and the controls that protect it. This inventory provides the basis for reviewing firewall rules, gateway policies and filtering requirements.
Telecom network segmentation can separate management, service and other network zones where appropriate. Segmentation limits unnecessary reachability and may help contain the impact of a compromised component. Review traffic flows whenever a new service, vendor, interface or interconnect is introduced.
Restrict access to approved sources, destinations and services. Review firewall rules, access-control lists, management paths and signaling gateway policies for broad or outdated permissions. Remove unused rules and accounts, validate trusted peers, and log administrative access. Changes should have an owner, a business justification and a defined review date.
IMS access security should also account for emergency and operational access. Document break-glass procedures, limit who can use them, and review activity afterward so urgent access does not become a permanent exception.
IMS traffic filtering should permit expected signaling flows and restrict messages or sources that violate the approved policy. Where supported, protocol-aware controls can validate message characteristics and apply rules based on expected behavior. Filtering can be complemented by rate limits and anomaly detection to help identify repeated requests, unusual message patterns or abnormal traffic volumes.
Policies must be tested carefully. Overly strict rules can block legitimate signaling or affect critical services, while overly permissive rules may leave avoidable exposure. Use controlled change processes, monitor results and maintain rollback procedures.
IPsec in VoLTE may protect selected IP communication paths through confidentiality, integrity and peer authentication, depending on the architecture and configuration. It can support IMS signaling protection, but it does not replace access control or traffic filtering. An authenticated peer may still send unexpected or harmful traffic, and IPsec security limitations mean that only covered traffic receives the configured protection.
Validate which paths are protected, whether peer definitions and key management follow approved guidance, and whether other controls still restrict what authenticated systems may do. Treat IPsec as one layer in a broader VoLTE security design.
VoLTE security hardening includes removing unnecessary services, restricting management interfaces, patching supported software, protecting credentials and maintaining approved configuration baselines. IMS security policies should define how rules are created, approved, reviewed, documented and retired. Regularly compare deployed settings with the approved baseline to identify configuration drift.
Monitoring helps teams identify traffic that does not match expected patterns. Review denied connections, unexpected sources, repeated authentication failures, signaling errors, unusual request rates and changes in service health. Correlate these events with network changes and operational activity to reduce false positives and support faster investigation.
Define escalation contacts, evidence-handling procedures and service-protection steps before an incident occurs. Traffic controls are most effective when network operations and security teams can respond consistently to alerts.
Regular reviews should verify that filtering and access rules still match the network design. Assess firewall and gateway policies, segmentation, trusted-peer definitions, logging, IPsec coverage where used, and exceptions. Use authorized, scoped testing that protects production services, then document findings, assign remediation owners and retest important changes.
Conclusion
VoLTE traffic filtering and access controls help prevent unauthorized network communication by limiting who can connect, which flows are permitted and how unusual traffic is handled. Operators should combine an accurate IMS security architecture with least-privilege access, signaling-aware filtering, segmentation, appropriate IPsec protection, component hardening and monitoring. Regular testing and clear IMS security policies help keep these controls aligned with evolving network requirements.