Blog
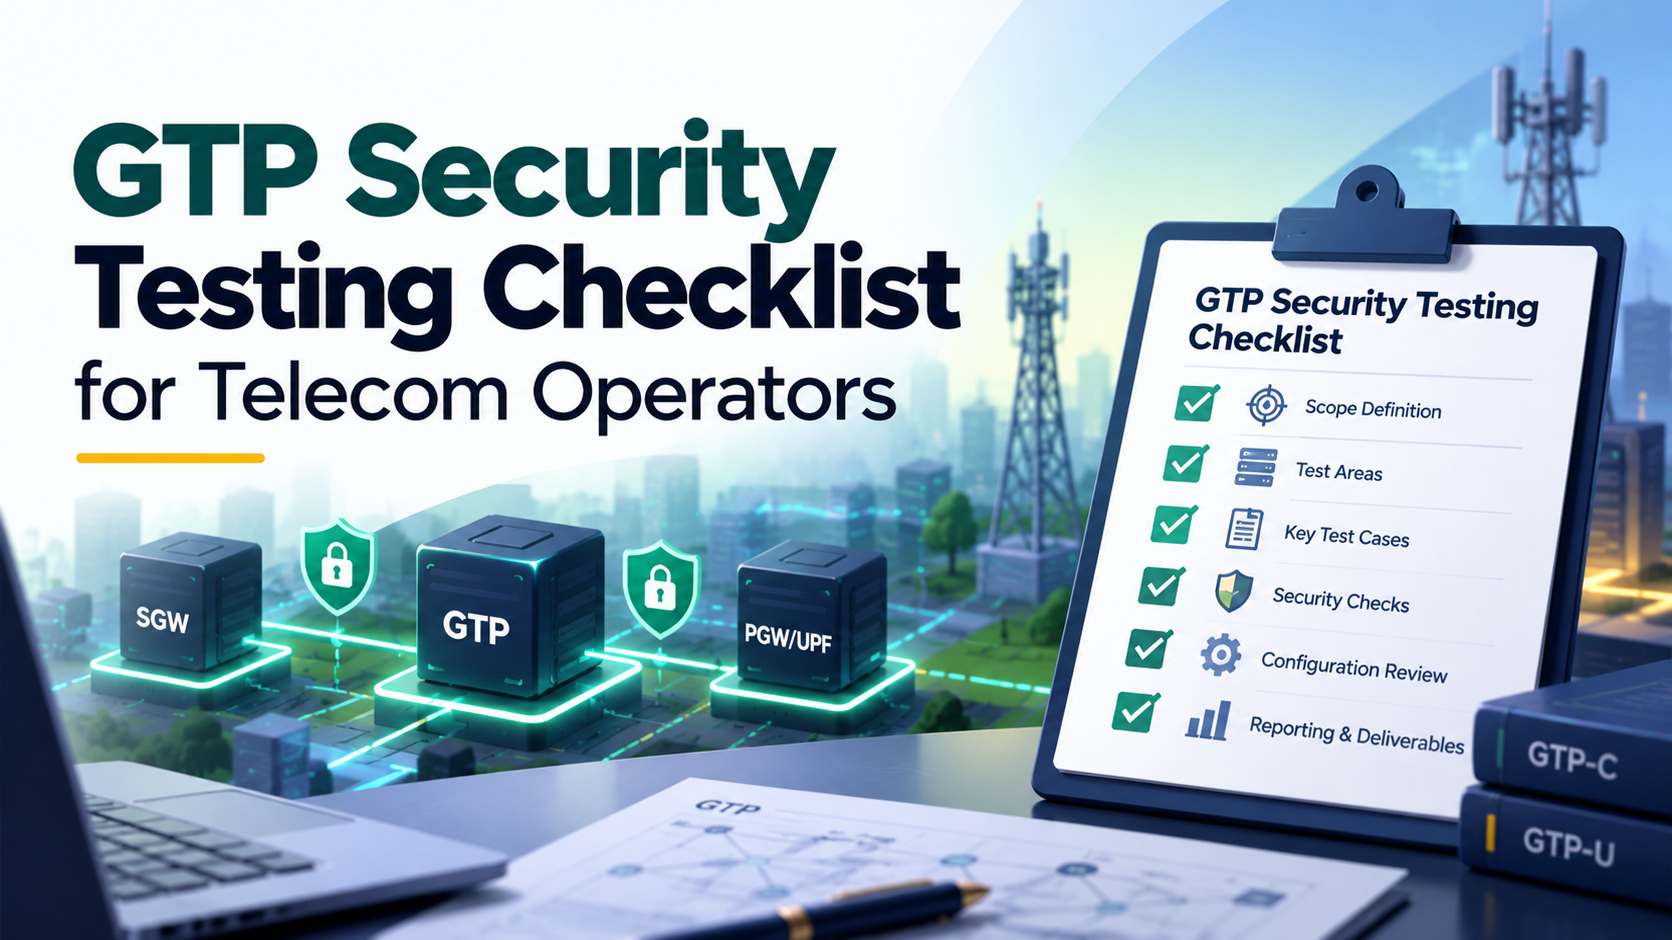

Mobile network operators rely on the GPRS Tunnelling Protocol (GTP) to support subscriber sessions and data communication across mobile packet-core networks. However, exposed interfaces, insufficient message validation, weak access controls, and configuration gaps can introduce security risks that affect network availability and operational resilience.
A GTP security testing checklist helps telecom operators review these areas systematically, identify weaknesses, and prioritize corrective actions. It can support routine security reviews, a GTP vulnerability assessment, a GTP security audit, or a more focused penetration-testing engagement.
This guide provides a practical checklist covering scope definition, interface discovery, protocol validation, security controls, risk analysis, reporting, and remediation.
A GTP security testing checklist is a structured set of checks used to evaluate the security of GTP-enabled network elements, interfaces, and configurations.
The checklist should reflect the operator's network architecture, applicable protocol versions, and testing objectives. It should also distinguish between reviewing a control, testing its behavior, and validating whether a weakness can be exploited.
A comprehensive telecom security assessment may combine configuration reviews, GTP interface testing, message-validation checks, access-control testing, and authorized penetration testing.
Use the following checklist as a starting point. Actual tests should be selected according to the approved scope and performed by authorized personnel.
Before testing begins, establish clear boundaries and identify the systems in scope.
Objective: Ensure that testing is complete enough to be useful without creating unnecessary operational risk.
Interface exposure can increase the attack surface if systems are reachable from unauthorized sources.
Objective: Reduce unnecessary exposure and limit opportunities for unauthorized signaling.
Network elements should validate incoming messages according to the relevant protocol requirements, session context, and security policies.
Objective: Determine whether message handling is consistent with expected protocol behavior and security requirements.
Access controls help ensure that only approved network elements communicate across designated interfaces.
Objective: Prevent unnecessary trust and restrict communication to legitimate network requirements.
GTP security testing should account for the protocol versions and functions deployed in the operator's environment.
GTPv1 is used for relevant user-plane tunneling and certain legacy control-plane applications, while GTPv2-C supports control-plane session management in LTE EPC environments. These roles should not be treated as interchangeable.
Objective: Ensure that testing reflects the actual network implementation rather than assuming all GTP traffic behaves identically.
Security controls should restrict unwanted traffic and help operators identify suspicious signaling activity.
Objective: Evaluate whether preventive and detective controls are appropriately configured and operational.
Not every unusual response or configuration issue represents an exploitable vulnerability. Findings should be validated before being prioritized.
Objective: Help operators focus resources on the most significant and actionable risks.
A useful assessment must translate technical findings into practical actions.
Objective: Turn assessment results into measurable security improvements.
These activities are related, but they serve different purposes.
A checklist can support all four activities, but it does not replace a defined methodology or guarantee that every vulnerability will be discovered.
For deeper testing, GTP security testing services may combine interface checks, message validation, access-control reviews, and controlled investigation of selected attack paths. A broader telecom penetration testing or signaling security assessment engagement may also cover other protocols when included in the agreed scope.
Operators should establish a testing schedule based on their architecture, risk profile, and operational requirements. Reviews are especially useful after significant network changes, new interconnections, configuration updates, or the discovery of relevant vulnerabilities.
The checklist should also be updated as network environments and security requirements evolve. It is most effective when used as part of an ongoing security program rather than as a one-time exercise.
A structured GTP security testing checklist helps telecom operators evaluate interface exposure, message validation, access controls, protocol-specific behavior, filtering, and monitoring. Combined with risk-based reporting and retesting, it provides a practical foundation for improving mobile core network security.
Matrix Shell Technologies' Signaling Security Testing service page is a relevant starting point for organizations exploring telecom signaling security assessments. A clearly scoped assessment can help identify gaps, prioritize remediation, and strengthen network resilience.