
Blog
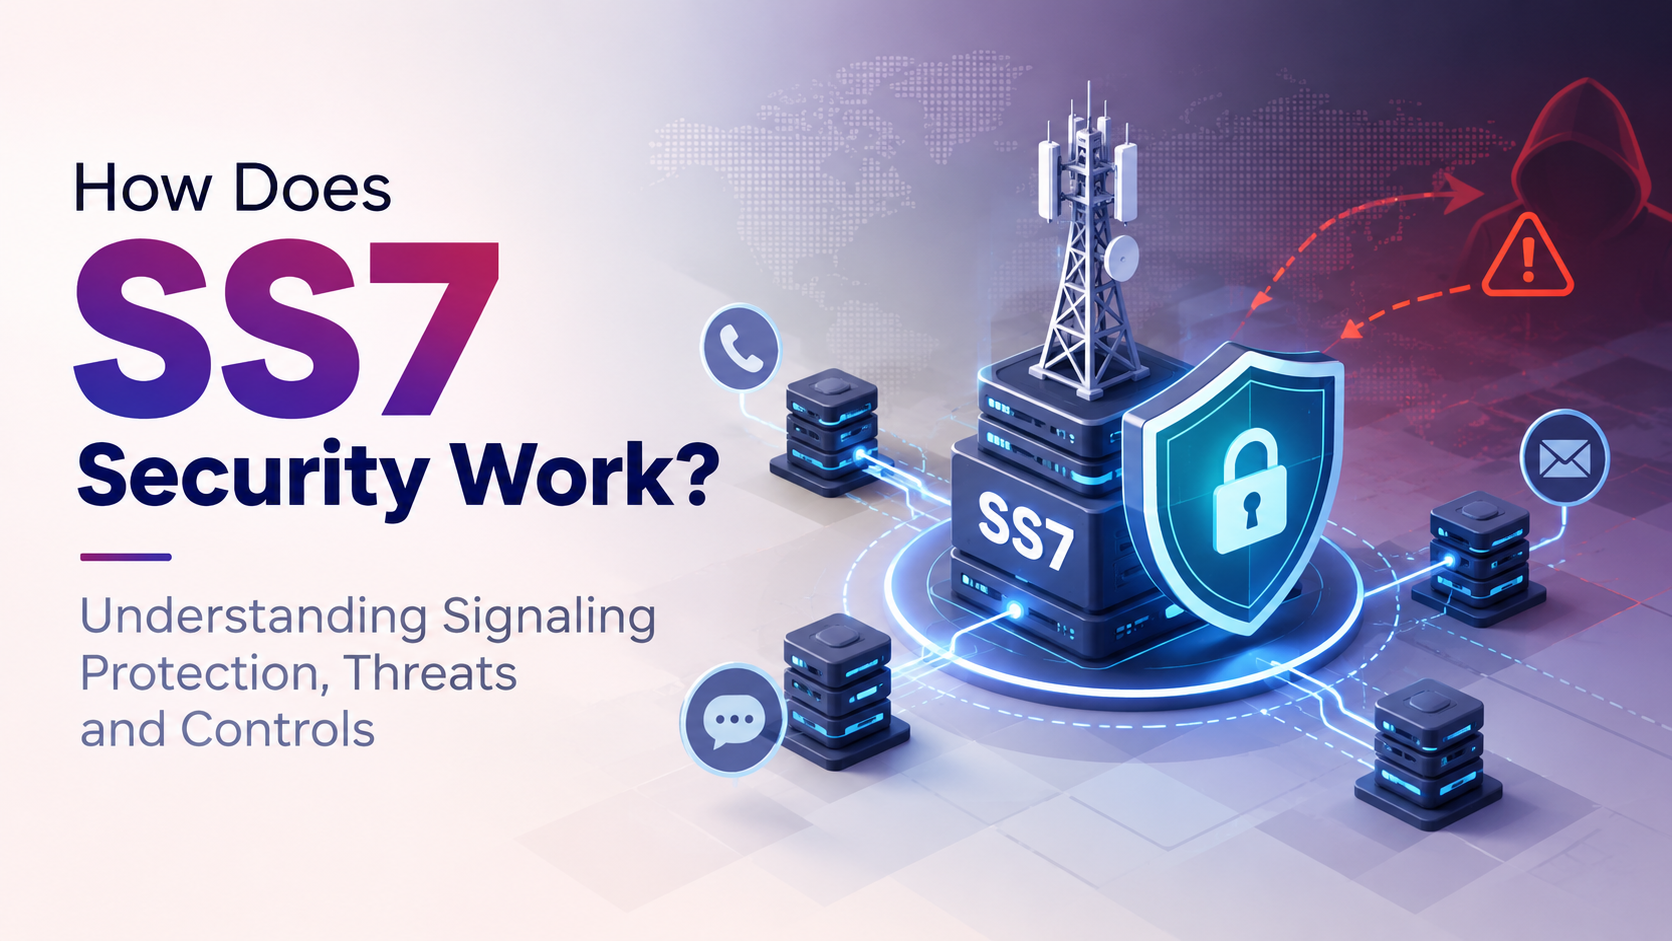
SS7 security works by protecting the signaling processes that allow telecom networks to authenticate subscribers, route calls and SMS messages, support roaming, and exchange network information. It combines SS7 security controls, signaling traffic monitoring, filtering, access restrictions, validation, and security testing to reduce the risk of unauthorized signaling activity.
Unlike traditional network security, SS7 security focuses heavily on the signaling layer—the control-plane communication that tells telecom networks what actions to perform. Because SS7 was designed around trusted relationships between network operators, modern telecom environments need additional SS7 protection mechanisms to address today’s threat landscape.
SS7 remains relevant across telecom environments that use legacy 2G and 3G infrastructure, roaming arrangements, interconnects, and fallback mechanisms. It can also interact with newer network generations as operators operate multi-generation environments.
This creates an important security challenge: protecting a modern mobile network requires visibility into legacy signaling as well as newer protocols.
Common SS7 security risks include:
These risks are part of the broader signaling security challenge affecting SS7, Diameter, GTP, and 5G signaling environments. Matrix Shell’s Signaling Security Testing service evaluates signaling security across 2G, 3G, 4G, and 5G networks.
Effective SS7 security typically involves several complementary layers. No single control can address every signaling threat, so operators need a combination of prevention, monitoring, validation, and testing.
The first step in SS7 protection is understanding how signaling moves through the network.
Telecom operators need visibility into:
Mapping these relationships helps identify where trusted signaling enters the environment and where security controls need to be applied.
This becomes particularly important in multi-generation networks, where SS7, Diameter, GTP, and 5G signaling systems may coexist. Matrix Shell’s signaling security strategy guidance highlights the need to understand interconnected signaling layers across 2G, 3G, 4G, and 5G networks.
One of the most important SS7 security controls is the ability to distinguish legitimate signaling activity from suspicious or unauthorized requests.
Traffic filtering can evaluate signaling messages based on factors such as:
The objective is to prevent unauthorized signaling requests from reaching sensitive network functions.
SS7 protection also depends on continuous visibility.
Monitoring signaling traffic can help operators identify unusual patterns, unexpected requests, and potentially malicious behavior. For example, repeated requests involving subscriber information or abnormal signaling activity may indicate an attempt to exploit signaling weaknesses.
Monitoring is particularly valuable because attackers may abuse legitimate signaling functionality rather than relying on traditional malware or endpoint-based techniques.
A comprehensive SS7 security strategy can include multiple controls working together.
Filtering helps block signaling messages that do not meet defined security or policy requirements.
Access restrictions help ensure that only authorized signaling entities and connections can interact with protected network functions.
Validation checks whether signaling requests are consistent with expected network behavior and configuration.
Continuous monitoring provides visibility into signaling activity and helps identify anomalies.
Security testing validates whether the deployed controls actually resist relevant attack scenarios and identifies weaknesses that may not be visible through configuration reviews alone.
These controls should be considered as part of a broader telecom signaling security strategy rather than as isolated mechanisms.
Effective SS7 protection can help reduce exposure to several common signaling threats.
Attackers may attempt to abuse signaling requests to obtain information that can reveal a subscriber’s location.
SS7 weaknesses can potentially be abused to interfere with SMS delivery, creating risks for sensitive communications and authentication messages.
Signaling abuse may allow attackers to attempt call redirection or other forms of communication manipulation.
Malicious signaling activity can generate excessive or unauthorized requests that affect network availability.
Signaling weaknesses can contribute to telecom fraud by enabling unauthorized access to network functions or subscriber-related information.
Understanding these vulnerabilities is essential before selecting appropriate controls. Matrix Shell’s guide on Understanding Signaling Vulnerabilities in Telecom Networks explains how weaknesses across SS7, Diameter, GTP, and 5G signaling can affect modern telecom environments.
Security controls should not simply be deployed and assumed to be effective. SS7 security testing helps operators validate whether signaling protections work as intended.
Testing can identify:
A structured assessment can also help determine whether security controls are capable of mitigating realistic signaling attack scenarios.
Matrix Shell’s Signaling Security Testing service provides multi-protocol assessment across SS7, Diameter, GTP, and 5G HTTP/2 interfaces, with coverage spanning 2G, 3G, 4G, and 5G environments.
Telecom networks are continuously changing. New roaming relationships, network upgrades, configuration changes, interconnections, and technology deployments can introduce new signaling exposure.
As a result, SS7 security should not be treated as a one-time configuration exercise.
A stronger approach combines:
This approach becomes even more important when SS7 exists alongside Diameter, GTP, and 5G signaling technologies.
SS7 protection is one component of a larger telecom signaling security strategy.
In multi-generation networks, operators may need to secure:
Each protocol introduces different security considerations. Protecting only one layer can therefore leave gaps elsewhere in the signaling ecosystem.
A unified approach helps operators evaluate signaling security across the complete network rather than treating individual protocols as isolated environments.
Understanding how SS7 security works is essential for telecom operators that continue to rely on SS7 across legacy networks, roaming, and interconnect environments.
Effective SS7 security controls combine traffic filtering, access management, message validation, monitoring, and security testing. Together, these measures provide stronger SS7 protection against signaling abuse, subscriber privacy risks, fraud, interception, and service disruption.
As telecom networks become increasingly interconnected across 2G, 3G, 4G, and 5G, operators should evaluate SS7 alongside other signaling protocols as part of a unified security strategy.
To identify vulnerabilities and validate signaling defenses across legacy and modern environments, explore Matrix Shell’s Signaling Security Testing capabilities.




