
Blog
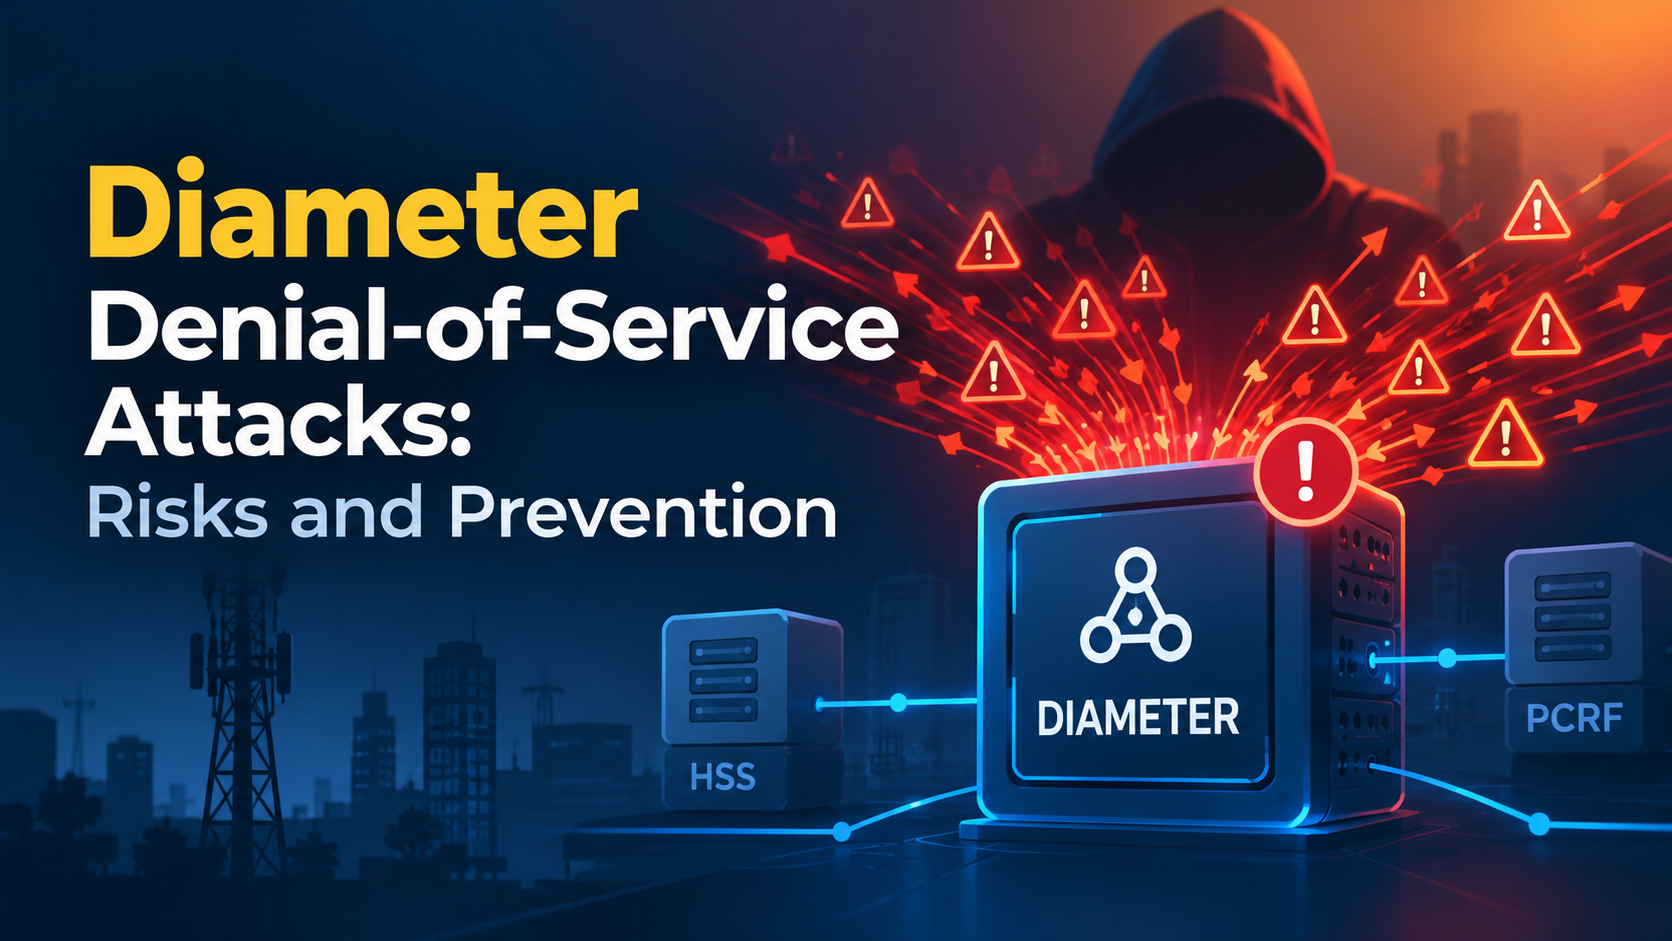
Diameter is a critical signaling protocol used in 4G/LTE networks for authentication, authorization, mobility management, subscriber services, accounting, and roaming. Because Diameter signaling supports important network functions, attacks that affect the availability of Diameter nodes can have consequences beyond the signaling layer itself.
One such threat is a Diameter denial of service attack, commonly referred to as Diameter DoS.
A Diameter DoS attack attempts to overwhelm or disrupt Diameter infrastructure through excessive, abnormal, malformed, or otherwise unauthorized signaling. The resulting impact depends on the operator's architecture, network capacity, filtering controls, and the specific Diameter functions being targeted.
GSMA's Diameter security research has documented denial-of-service as a potential threat in Diameter networks, while its current security resources maintain dedicated guidance for Diameter interconnect attacks and countermeasures.
A Diameter denial-of-service attack is an attempt to reduce the availability or responsiveness of Diameter-dependent network services by generating traffic or signaling that consumes network resources.
A DoS condition can potentially affect:
The objective does not necessarily have to be taking an entire network offline. Even increased latency, resource exhaustion, or failure to process legitimate signaling can create operational problems.
Diameter itself is designed to support reliable transport and signaling in local and roaming environments. RFC 6733 defines Diameter's message, transport, routing, and security mechanisms and requires secured transport using TLS, DTLS, or IPsec.
A Diameter DoS condition can result from different types of traffic and abuse.
An attacker may generate a high volume of Diameter requests in an attempt to consume processing resources.
If sufficient controls are not in place, excessive requests can increase:
The actual impact depends on the capacity and architecture of the targeted network elements.
Attackers may also send malformed or unexpected messages to test how Diameter implementations respond.
Examples include messages containing:
RFC 6733 defines error handling for conditions including invalid message length and invalid AVP flag combinations.
From a security perspective, operators should verify that invalid traffic is rejected safely without causing instability or excessive resource consumption.
Diameter message manipulation can become relevant to availability attacks when modified or crafted messages trigger excessive processing or unexpected network behavior.
For example, security testing may examine how systems handle:
This does not mean every manipulated message causes a DoS condition. The objective of testing is to determine whether deployed security controls and network elements handle abnormal signaling safely.
This is one reason Diameter security vulnerabilities should be evaluated from both a confidentiality/integrity perspective and an availability perspective.
Diameter spoofing can also contribute to denial-of-service risk.
If an unauthorized system can successfully appear to be a trusted Diameter peer, it may have a greater opportunity to generate signaling that would normally be restricted.
Potential consequences can include:
Strong peer authentication and authorization therefore form an important part of Diameter DoS prevention.
RFC 6733 distinguishes peer authentication from authorization and includes requirements around authorized Diameter peers.
Several Diameter attack vectors can potentially contribute to availability problems.
High-Volume Signaling
Large numbers of requests may consume processing or connection resources.
Repeated Requests
Repeated signaling toward the same service or subscriber can increase processing requirements.
Malformed Messages
Unexpected messages may stress protocol-processing components if not safely handled.
Unauthorized Peers
Traffic from unauthorized sources can increase exposure if peer controls are weak.
Roaming and Interconnect Abuse
External Diameter relationships can introduce additional traffic sources that need to be controlled.
Message Manipulation
Unexpected signaling content may trigger unnecessary processing or error handling.
Resource Exhaustion
Repeated connections or requests can consume finite network resources.
GSMA's Diameter security research identified subscriber denial of service as a possible threat in Diameter networks and reported successful attacks involving denial-of-service conditions in its tested networks.
LTE Diameter vulnerabilities are not limited to one interface or one type of attack.
Diameter is used across different LTE functions and interfaces, so an availability issue affecting a signaling component can potentially influence dependent services.
Relevant areas for assessment may include:
The exact risk depends on how each interface is deployed.
A Diameter security assessment should therefore consider both internal and external signaling paths.
Roaming is particularly important because Diameter traffic may cross operator and interconnect boundaries.
A typical signaling path may involve:
Home Network → IPX / Interconnect → Visited Network
Each boundary introduces a security-control point.
GSMA specifically maintains Diameter Interconnect Security (FS.19) guidance covering potential Diameter-based attacks on mobile networks and customers and countermeasures for LTE and 5G interconnection security.
Operators should therefore assess:
Detection should combine traffic monitoring with signaling-level visibility.
1. Monitor Signaling Volume
Establish normal traffic baselines and look for significant deviations.
2. Detect Abnormal Request Rates
Repeated requests from the same source, peer, application, or subscriber context can warrant investigation.
3. Monitor Unknown Peers
Unexpected Diameter connection attempts may indicate configuration problems or unauthorized activity.
4. Track Error Responses
An unusual increase in Diameter errors can indicate malformed or unexpected signaling.
5. Monitor Resource Utilization
Track:
6. Correlate Signaling and Network Events
A signaling spike combined with resource exhaustion provides stronger evidence than either indicator alone.
A layered approach is essential.
Peer Authentication and Authorization
Restrict Diameter connections to approved and authorized peers.
Protected Transport
Use appropriate transport security. RFC 6733 requires Diameter implementations to support secured transport and states that Diameter must not be used without TLS, DTLS, or IPsec.
Diameter Firewall
Apply policies that restrict unauthorized peers, applications, messages, and traffic patterns.
Rate Controls
Limit excessive signaling where appropriate to prevent abnormal traffic from consuming disproportionate resources.
Message Filtering
Filter malformed, unauthorized, or policy-violating messages.
Network Segmentation
Restrict access to critical Diameter infrastructure.
Monitoring and Alerting
Detect unusual signaling and resource-consumption patterns early.
Resilience and Failover
Where supported, ensure critical services have appropriate redundancy and recovery mechanisms.
Diameter security testing can help operators evaluate whether their controls can withstand controlled abnormal signaling.
A structured assessment may include:
1. Architecture Review
Identify Diameter nodes, interfaces, peers, applications, and trust boundaries.
2. Configuration Review
Evaluate authentication, authorization, filtering, rate controls, and network exposure.
3. Diameter Vulnerability Assessment
Identify weaknesses that could contribute to availability problems.
4. Controlled Traffic Testing
Within an approved test environment, evaluate how network elements handle abnormal signaling volumes and malformed messages.
5. Diameter Penetration Testing
Validate selected weaknesses through controlled and carefully scoped attack scenarios.
6. Detection Validation
Confirm that monitoring and alerting systems identify suspicious signaling.
Testing should be carefully scoped and preferably conducted using dedicated test subscribers and controlled conditions to avoid affecting live users.
| Area | What to Check |
|---|---|
| Peer Security | Authorized Diameter peers |
| Authentication | Strong peer authentication |
| Authorization | Appropriate peer permissions |
| Traffic | Normal and abnormal signaling rates |
| Messages | Final TakeawayDiameter DoS, or Diameter denial of service, is an availability threat that can arise from excessive, malformed, unauthorized, or otherwise abnormal Diameter signaling. The risk becomes more significant when operators have weak peer controls, insufficient filtering, limited monitoring, or poorly protected roaming and interconnect boundaries. Importantly, DoS should not be considered in isolation. It can be connected with broader Diameter security vulnerabilities, Diameter attack vectors, Diameter message manipulation, and Diameter spoofing risks. A comprehensive Diameter security assessment should therefore evaluate the entire signaling environment—from trusted peers and transport security to message validation, traffic controls, monitoring, and resilience. Recommended internal links For the final published article, I recommend these two internal links:
Recommended SEO journey: Diameter DoS → Diameter Attack Vectors → Diameter Vulnerabilities → Diameter Security Testing → Service Page I have kept these as anchor recommendations because the exact Matrix Shell URLs were not provided. Recent PostFrequently Asked QuestionsWhat is a Diameter denial-of-service attack?What is Diameter DoS?What are common Diameter DoS attack vectors?Can Diameter message manipulation cause DoS?Can Diameter spoofing contribute to denial of service? 5130/6020 Marvel Fuego, Opp Seasons Mall, Magarpatta,Hadapsar, Pune , MH, India, 411028.      |