
Blog
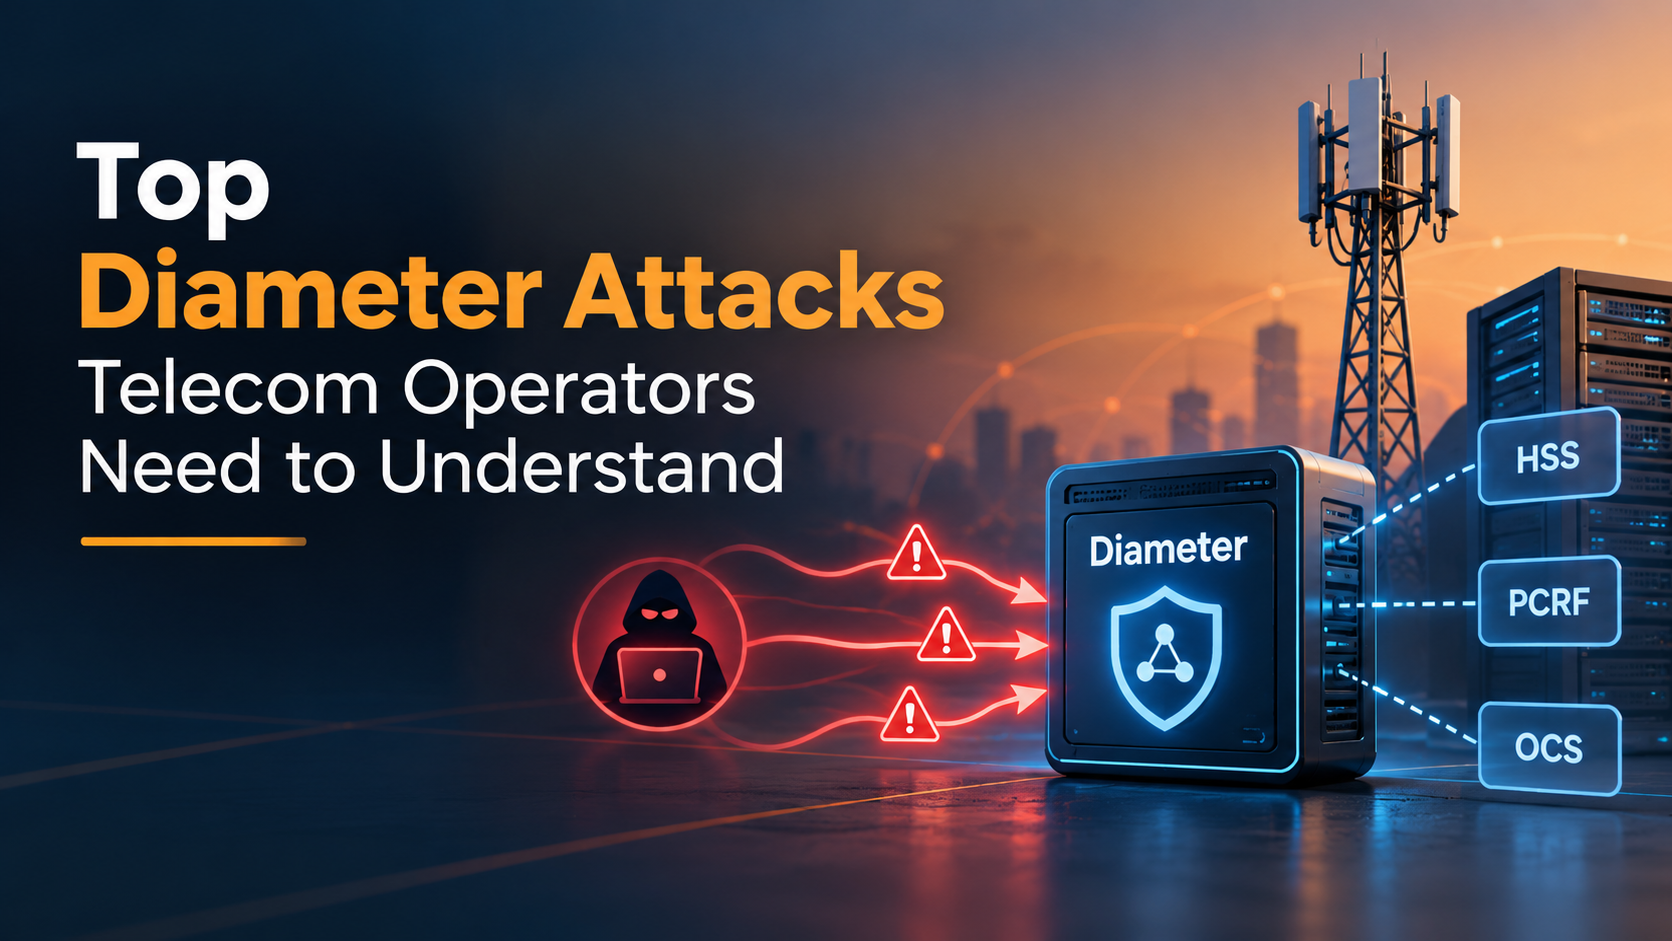
Diameter is a critical signaling protocol used across 4G/LTE networks for authentication, authorization, mobility management, subscriber services, and roaming. It replaced several limitations of earlier signaling technologies, but its security still depends heavily on how Diameter networks are designed, configured, connected, and monitored.
This makes understanding Diameter attacks important for telecom operators.
Diameter-related threats can involve unauthorized signaling, message manipulation, peer spoofing, subscriber information exposure, and denial-of-service conditions. The risk can become more significant when Diameter signaling crosses operator boundaries through roaming and interconnect environments.
GSMA maintains dedicated guidance on Diameter Interconnect Security that addresses potential Diameter-based attacks against mobile networks and customers and describes relevant countermeasures.
Diameter attacks are attempts to abuse weaknesses in Diameter signaling, network configurations, trusted relationships, or security controls to obtain unauthorized access, manipulate signaling, expose information, or disrupt services.
An attack does not necessarily require a flaw in the Diameter protocol itself.
Risk can arise from:
RFC 6733 defines security mechanisms and requirements for Diameter communications, including protected transport and peer authorization.
Diameter message manipulation involves influencing signaling messages so that network elements process unexpected or unauthorized information.
Diameter messages contain Attribute-Value Pairs (AVPs), which carry information used by network applications.
If message validation is insufficient, attackers may attempt to manipulate:
The potential impact depends on the affected Diameter application and network element.
For example, unauthorized signaling could potentially influence authentication, mobility, or subscriber-related procedures.
Operators should validate:
RFC 6733 specifies validation requirements for Diameter messages and routing information.
Diameter spoofing involves attempting to make a signaling message or connection appear to originate from a trusted Diameter peer.
This is particularly relevant because Diameter networks depend on relationships between trusted network elements.
If peer authentication or authorization is weak, an unauthorized system could potentially attempt to communicate with Diameter infrastructure while appearing to be a legitimate participant.
Potential targets include:
Key controls
Operators should implement:
RFC 6733 includes requirements around peer authorization and secured Diameter communications.
Another category of Diameter attack vectors involves sending signaling requests that should only originate from authorized network elements.
For example, an attacker who gains access to a signaling path could attempt to generate requests associated with authentication, subscriber information, or mobility functions.
The security concern is not simply whether a request is technically valid. The network should also determine whether the source is authorized to make that request.
A Diameter security assessment can therefore examine:
Some Diameter security vulnerabilities can create opportunities for unauthorized access to subscriber-related information.
Depending on the application and implementation, Diameter signaling may carry information related to:
Improper access controls or message filtering can increase the possibility of unauthorized information requests.
For telecom operators, this makes subscriber-data protection an important part of Diameter security testing.
Diameter signaling supports mobility-related functions, making location-related information another area requiring protection.
An attacker who can generate unauthorized signaling requests may attempt to obtain information associated with a subscriber's mobility or network location.
Potential risks include:
The exact exposure depends on the operator's architecture, Diameter applications, and security controls.
A Diameter vulnerability assessment can help identify whether these requests are appropriately restricted.
Diameter supports several authentication and subscriber-management procedures.
Weak authorization or message validation could potentially allow unauthorized signaling to influence subscriber-related network behavior.
This can create risks involving:
GSMA has published research describing Diameter-related attack scenarios involving S6a signaling and subscriber-related network behavior.
This highlights why operators should assess not only the Diameter transport layer but also the applications and commands running over it.
Diameter DoS, or Diameter denial of service, is an attack category focused on availability.
An attacker may attempt to generate excessive or abnormal signaling that consumes resources on Diameter nodes or dependent network elements.
Potential symptoms can include:
A Diameter security assessment can evaluate whether the environment has appropriate controls for detecting and handling abnormal signaling volumes.
These may include:
Attackers may also attempt to send malformed or unexpected Diameter messages to identify weaknesses in protocol implementations or network elements.
Testing can examine how systems handle:
The objective is to determine whether malformed traffic is safely rejected rather than causing unexpected behavior.
This is one area where Diameter penetration testing can complement a vulnerability assessment.
One of the most important Diameter attack vectors exists at inter-operator boundaries.
Diameter roaming can involve:
Home Operator → IPX/Interconnect → Visited Operator
Every additional trust relationship can create another security boundary that needs to be controlled.
Potential concerns include:
GSMA specifically addresses Diameter interconnect security and countermeasures for inter-operator environments.
Therefore, Diameter security testing should not be limited to the internal core network.
Diameter requires appropriate protection for communications.
RFC 6733 specifies that Diameter must not be used without TLS, DTLS, or IPsec protection.
A security review should therefore examine:
Transport protection is an important foundation, but it does not eliminate application-level Diameter attacks.
A layered approach to Diameter security testing can help operators identify weaknesses and suspicious activity.
Architecture Assessment
Map Diameter nodes, interfaces, peers, applications, routing paths, and trust boundaries.
Configuration Review
Review authentication, authorization, transport security, filtering, access controls, and network exposure.
Diameter Vulnerability Assessment
Identify weaknesses that could potentially be exploited.
Diameter Penetration Testing
Use controlled attack scenarios to validate selected weaknesses.
Signaling Monitoring
Monitor for:
This combination provides better visibility than relying on a single security control.
Telecom operators can strengthen their Diameter security posture by:
Controls should be adapted to the operator's architecture, interfaces, roaming model, and risk environment.
The most important Diameter attacks are not limited to one specific technique. Operators should understand the risks associated with Diameter message manipulation, Diameter spoofing, unauthorized signaling, subscriber information exposure, location-related attacks, profile manipulation, malformed messages, roaming/interconnect weaknesses, and Diameter DoS.
Many of these attack scenarios are enabled not by a fundamental protocol flaw, but by weaknesses in authentication, authorization, filtering, configuration, trust relationships, or monitoring.
For that reason, operators should combine Diameter security testing, vulnerability assessment, security auditing, and controlled penetration testing to evaluate how effectively their LTE signaling environment can withstand realistic attack scenarios.
Recommended internal links
For the published article, I recommend:
Recommended SEO flow:
Diameter Attacks → Diameter Attack Vectors → Diameter Vulnerabilities → Diameter Security Testing → Service Page
I have kept these as anchor recommendations rather than inventing URLs because the exact Matrix Shell URLs were not provided.




