Blog
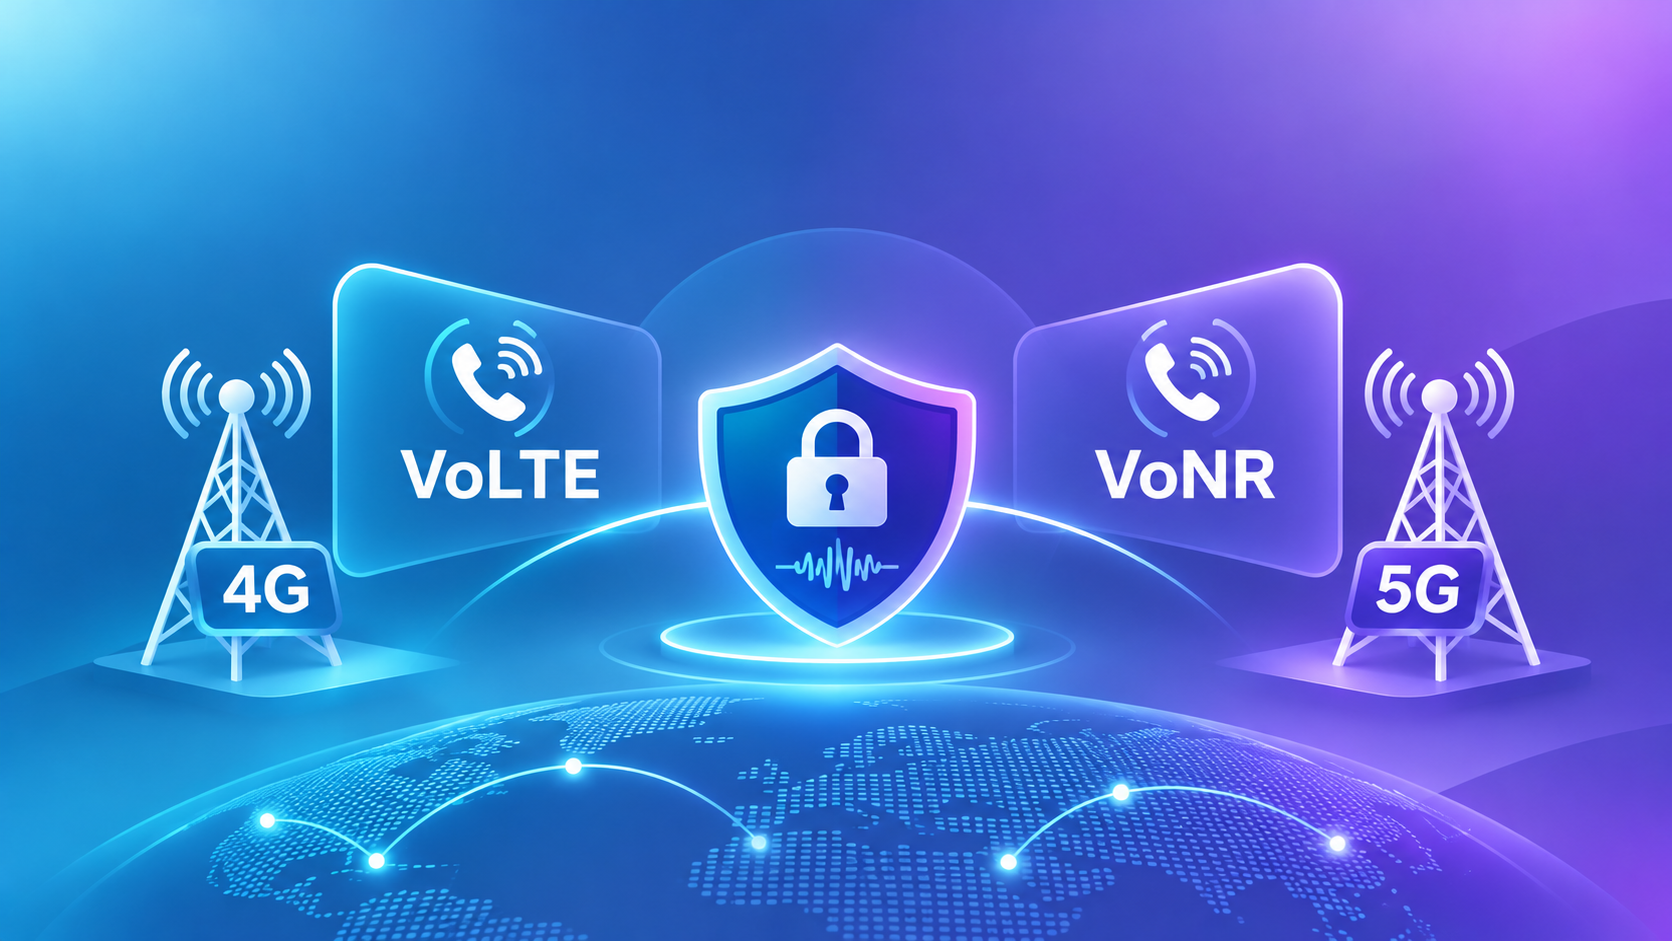
Voice services have moved from traditional circuit-switched networks to IP-based platforms. VoLTE delivers voice over 4G LTE, while VoNR supports voice over 5G New Radio. Both provide an important foundation for modern mobile communication, but they also introduce security considerations across access networks, core systems and operator interconnections.
VoLTE and VoNR security is not limited to protecting a single network element. Operators must secure signaling, subscriber access, roaming relationships and transitions between generations of mobile technology. A weakness in one part of the service path can affect call availability, subscriber privacy or trust between networks.
VoLTE uses LTE radio access and the IP Multimedia Subsystem (IMS) to establish and manage voice sessions. SIP is commonly used for session signaling, while supporting network functions handle subscriber registration, routing and service control.
VoNR uses 5G New Radio access for voice, with IMS continuing to provide the voice service framework in many deployments. The access technology changes, but operators still need to protect IMS functions, signaling exchanges and connections to other networks.
VoLTE vs VoNR should be compared across the complete service path. Both require secure identity handling, controlled signaling and reliable interconnection.
Although implementations differ, several risk categories affect both services:
Signaling abuse: malformed, unexpected or excessive SIP messages may affect registration, call setup or network resources.
Interface exposure: poorly restricted interfaces can create paths for unauthorized access or traffic.
Subscriber privacy: signaling and service data may expose identifiers or communication-related information if access and handling controls are weak.
Misconfiguration: inconsistent filtering, routing or access policies can create gaps between network zones or sites.
Denial of service: high volumes of abusive requests or resource exhaustion can reduce voice-service availability.
Interconnection weaknesses: partner links may introduce risk when trust, permitted traffic and monitoring are not clearly enforced.
These concerns affect 4G voice security and 5G voice security and should be assessed across the full architecture.
IMS network security is important because IMS supports voice service control across multiple access technologies. Protecting IMS means securing components, administrative access, signaling paths, configuration and the interfaces that connect to external operators.
VoLTE interconnect security and SIP interconnect security deserve particular attention where operators exchange signaling for roaming or other inter-operator services. Controls should restrict communication to approved partners and endpoints, validate messages, apply suitable rate limits and monitor unexpected traffic.
IMS roaming security and VoLTE roaming security also require clear partner governance. Operators should document which services and message types are permitted, how routes are maintained, who investigates suspicious activity and how incidents are escalated. These practices strengthen wider roaming network security and telecom interconnection security.
Network evolution rarely happens in one step. Operators may run LTE and 5G services together, maintain legacy voice arrangements and support subscribers moving between coverage areas. As a result, IMS security in 5G must be considered alongside existing LTE controls.
VoNR security should cover the 5G access environment, the IMS service layer and the interfaces used to reach other operators. Review authentication and access policies, signaling protection, network segmentation, configuration consistency and monitoring. Ensure that security controls remain effective when a call is established, transferred or routed through an interconnect.
VoLTE legacy network interworking may remain necessary during migration. LTE voice continuity and voice service continuity security depend on predictable transitions and correctly configured fallback behavior. Where circuit-switched fallback is used, CS fallback security should be included in the assessment. Validate that fallback does not bypass intended access restrictions, monitoring or privacy safeguards.
Telecom interworking security is therefore a cross-generation responsibility. A secure 5G deployment can still inherit exposure from older interfaces, partner links or transition procedures if those dependencies are not reviewed.
An IMS security assessment should evaluate the technical controls and operational processes that protect voice services. A practical scope can include:
Interface inventory: identify exposed interfaces, partner connections, endpoints and permitted traffic.
SIP and signaling validation: review message handling, routing behavior, filtering and rate limits.
Access and segmentation: confirm that external-facing systems are separated from internal IMS components and administrative access is restricted.
Configuration review: check security settings, redundancy, patch status and consistency across sites and vendors.
Roaming and interconnect review: verify partner authorization, route controls, responsibilities and escalation procedures.
Monitoring and response: assess logs, alerting, anomaly detection and incident coordination.
Testing should be formally authorized, scoped with relevant stakeholders and planned to avoid disruption to live voice services. Findings should explain the affected component, realistic impact, evidence, risk rating and recommended remediation. Retesting should verify that fixes are effective.
Begin by mapping voice-service dependencies across LTE, 5G, IMS, roaming and legacy environments. Identify which controls are shared and where different technologies require specific safeguards. Prioritize exposed interfaces and high-impact interconnections.
Next, validate access restrictions, SIP handling, filtering and monitoring. Review partner agreements alongside technical configurations so that documented trust relationships match actual network behavior. Include fallback and continuity scenarios in testing, not just standard call setup.
Make security reviews part of ongoing operations, repeating them after upgrades, new roaming agreements, vendor changes or routing modifications.
VoLTE and VoNR security requires a consistent approach across 4G, 5G, IMS, roaming and interconnect environments. Operators should protect signaling, restrict interfaces, govern partner relationships and test service transitions. A well-scoped IMS security assessment can identify weaknesses before they affect subscribers or service availability, helping maintain trusted voice communication throughout network evolution.