Blog
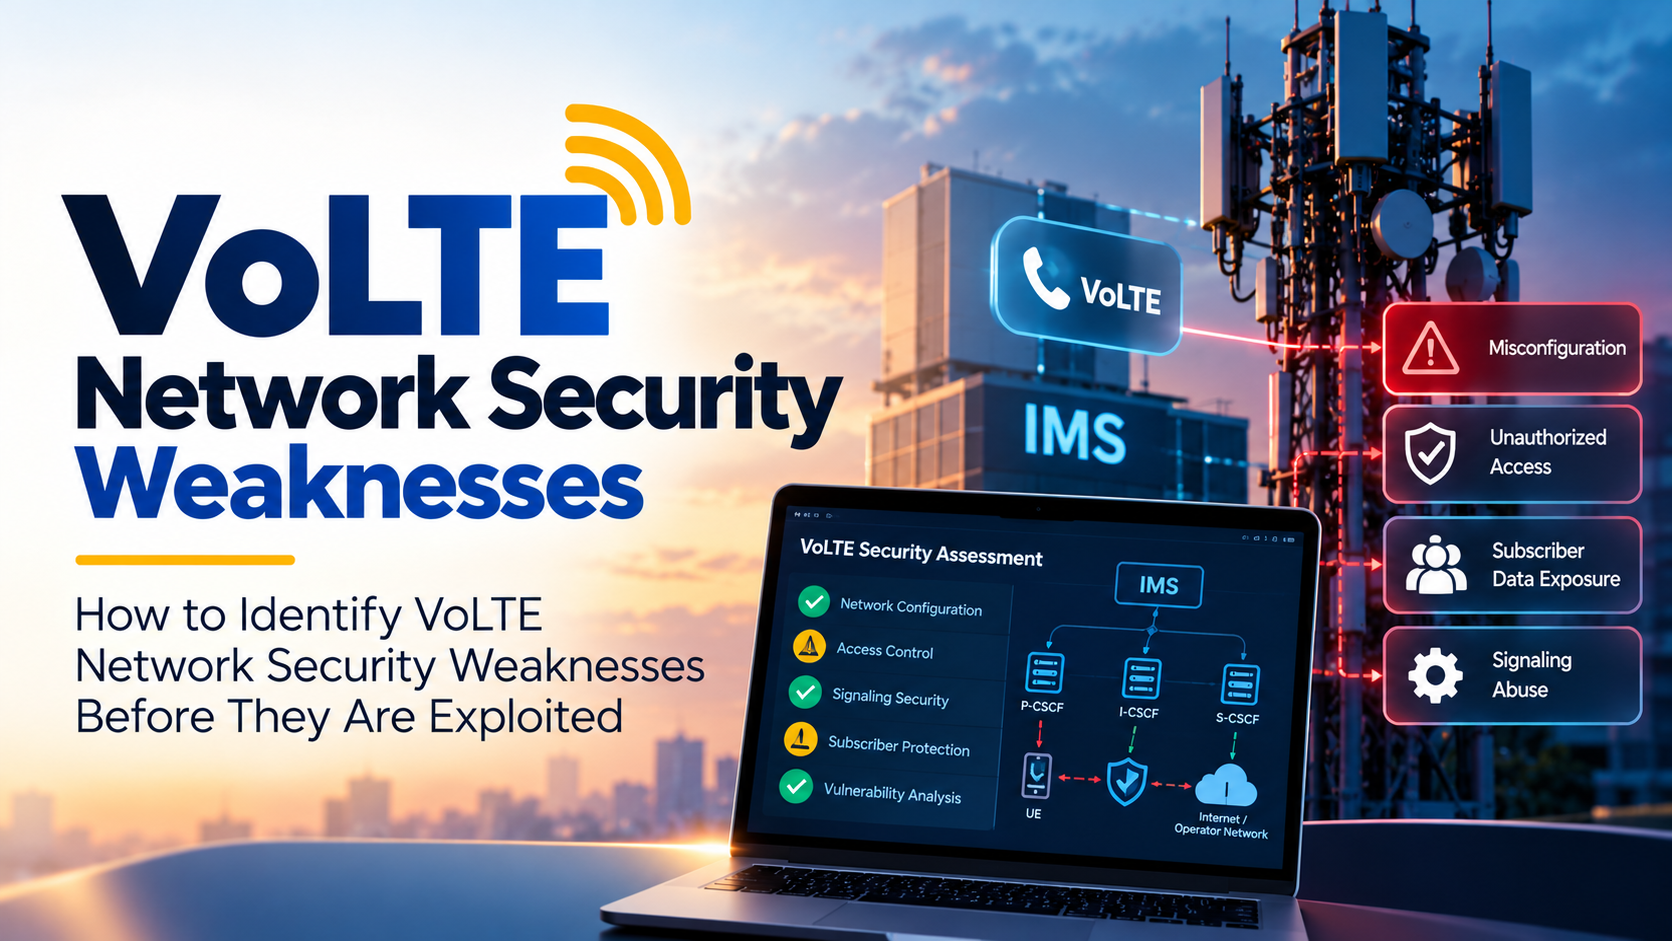
Voice over LTE (VoLTE) delivers voice services over LTE networks through IP-based communication and the IP Multimedia Subsystem (IMS). The architecture depends on multiple network functions, signaling paths, interfaces and access policies working together. If a control is misconfigured or a trust boundary is too permissive, a weakness may expose services, infrastructure or subscriber-related information.
Identifying VoLTE network security weaknesses early helps telecom operators reduce avoidable exposure and prioritise remediation. This guide explains where to look, how to conduct a structured VoLTE vulnerability assessment, and how IMS security testing and broader telecom security testing can help validate findings. The actual risks depend on each operator’s implementation and should be confirmed through authorised assessment.
VoLTE security is not limited to a single device or interface. Voice services rely on IMS components, signaling, routing, management access, interconnections and operational processes. A weakness in one area may create an unnecessary path into another, while limited monitoring can make suspicious activity harder to detect.
LTE voice security risks can affect availability, service integrity, infrastructure exposure or subscriber privacy, depending on the weakness and environment. A proactive review gives teams a chance to identify gaps before they are exploited, without assuming that every possible weakness exists in every network.
Start by documenting the architecture, relevant IMS components, interfaces, trust boundaries, external connections and management paths. Confirm which assets and environments are included, which are excluded, and what testing is authorised. Establish operational contacts, test windows, monitoring requirements and stop conditions before technical work begins.
A clearly documented scope helps ensure that the assessment examines the right exposure without unintentionally affecting unrelated systems. If the engagement includes wider telecom network security, list those additional domains explicitly.
Review how SIP signaling and related messages are validated, authenticated and handled. Check for overly permissive message processing, insufficient rate controls, unexpected request handling and gaps in security logging. VoLTE signaling vulnerabilities should be validated using approved test cases that match the architecture and avoid unnecessary service impact.
Examine whether traffic is restricted to approved sources, destinations and network functions. Broad allow rules, undocumented exceptions or unnecessary exposed interfaces may increase the attack surface. Confirm that external and partner-facing connections have appropriate boundaries and that filtering policies are maintained as the network changes.
Review administrative interfaces, role assignments, authentication, credential handling and configuration baselines. Unnecessary services, excessive privileges or weak change control can create avoidable exposure. Ensure that management access is restricted to approved systems and that changes are recorded and reviewable.
Assess whether critical IMS functions are separated from management systems and less-trusted environments. Verify that inter-segment traffic is limited to necessary communication paths. Poor segmentation can increase VoLTE infrastructure exposure if a less-trusted component is compromised.
Review access to subscriber identifiers, call-related metadata, logs and diagnostic output. Excessive permissions, unnecessary data retention or sensitive information in troubleshooting records may create subscriber privacy risks. IMS subscriber data protection should include least-privilege access, data minimisation, appropriate retention and protected logging.
Check whether relevant access events, signaling anomalies and configuration changes are logged and investigated. Confirm that logs are protected, time settings are consistent, alerts have clear owners and escalation procedures are documented. Monitoring gaps can delay response to suspicious activity.
A VoLTE vulnerability assessment should combine architecture and configuration review with evidence-based technical validation appropriate to the scope. Gather relevant documentation, identify exposed paths, review policies and test selected controls with permission. Record the asset, weakness, evidence, potential impact and recommended remediation for each finding.
IMS security testing may include access-control validation, signaling checks, segmentation review and authorised penetration testing. Broader telecom security testing can examine adjacent domains only when those systems are explicitly included. Avoid disruptive techniques unless they are specifically approved and supported by an operational safety plan.
Rank findings using severity, exploitability, exposure and potential service or subscriber impact. Assign remediation owners, target dates and a method for confirming the fix. Where immediate correction is not possible, document residual risk and any compensating controls. Retest important fixes to verify that the weakness has been addressed and that changes have not introduced new issues.
A practical IMS security checklist can help repeat the review over time. Include signaling controls, routing and filtering, access permissions, segmentation, configuration baselines, subscriber information security, monitoring and remediation status. Keep the checklist aligned with the actual implementation rather than treating it as a substitute for testing.
Identifying VoLTE network security weaknesses requires a structured review of signaling, interfaces, access policies, segmentation, configuration, subscriber information and monitoring. A risk-based VoLTE security assessment helps operators validate relevant gaps, prioritise fixes and reduce avoidable exposure. Matrix Shell can support telecom operators with tailored IMS security testing and telecom security testing aligned to their network architecture, operational requirements and agreed scope.